How a growing technology platform moved from a shared default VPC to a secure, production-ready AWS architecture
As the company’s containerized workloads and data-intensive services grew, its shared default VPC created security, isolation, monitoring, and scalability constraints. Flentas migrated the platform into dedicated AWS environments, separating staging and production while modernizing compute and databases and strengthening security controls—all in just three weeks with minimal business disruption.
- Network isolation between staging and production
- 100%
- Infrastructure protection and monitoring
- 24x7
- End-to-end migration completed
- 3 weeks
- Security, observability, and scalability built in
- Production-ready
A shared AWS environment creating security and scalability risks
The company's default VPC had become a constraint as the platform grew, making it harder to separate environments, secure workloads, and gain visibility into infrastructure performance.
No environment isolation
Staging and production workloads shared the same network environment.
Security gaps
Web protection, secrets management, threat detection, and configuration monitoring were not comprehensively implemented.
Limited observability
The absence of centralized dashboards and enhanced database monitoring made performance issues harder to identify.
Scalability constraints
The existing architecture wasn't designed to support the platform's longer-term growth.
A dedicated AWS architecture built for isolation, security, and scale
Flentas redesigned the environment around clear separation between workloads while modernizing the underlying infrastructure.
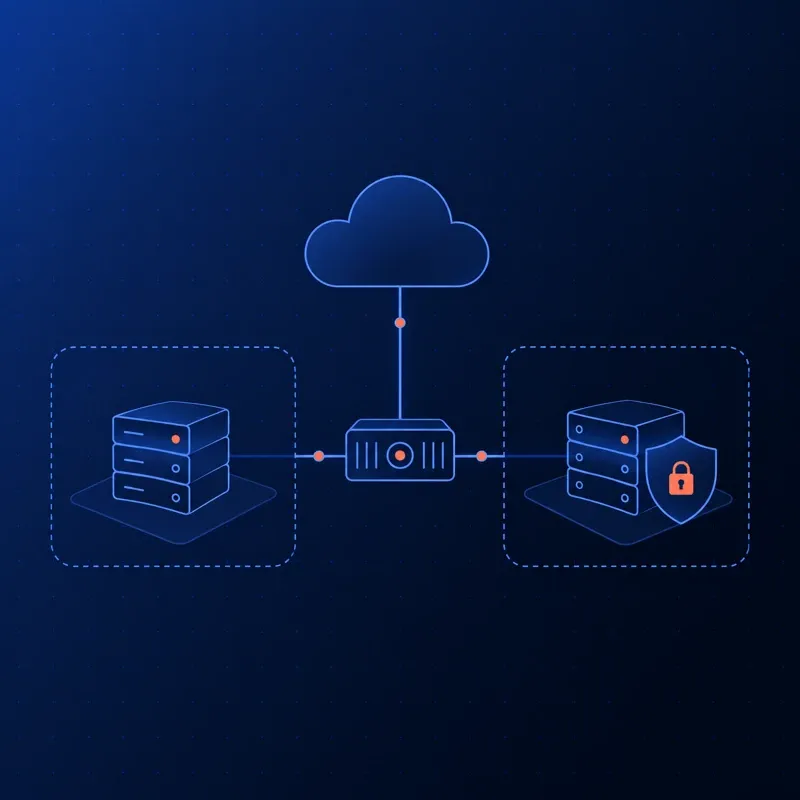
Created dedicated VPCs for staging and production, providing complete network isolation and environment-specific controls.
Migrated containerized applications to Amazon ECS Fargate and upgraded PostgreSQL to Amazon Aurora PostgreSQL for greater scalability and availability.
Implemented layered security using AWS WAF, GuardDuty, AWS Config, VPC Flow Logs, least-privilege IAM, and AWS Secrets Manager.
Centralized observability through CloudWatch dashboards, database monitoring, and SNS alerts, while optimizing content delivery through CloudFront and S3.
Isolated, secure, observable, and ready to scale
100% network isolation
Keeping staging and production completely separated.
24x7 infrastructure protection and monitoring
With centralized security and observability services.
Real-time infrastructure visibility
Enabling proactive detection and response to potential issues.
Improved scalability and resilience
With ECS Fargate and Aurora PostgreSQL reducing infrastructure management overhead.
Lower-latency global access
Supported by CloudFront and AWS Global Accelerator.
Three-week migration
Allowing the company to modernize its AWS environment while maintaining business continuity.
What technology teams usually ask about moving from shared to isolated AWS environments
Ready to move from shared infrastructure to a secure, isolated AWS architecture?
Talk to an AWS-certified architect about your own migration.